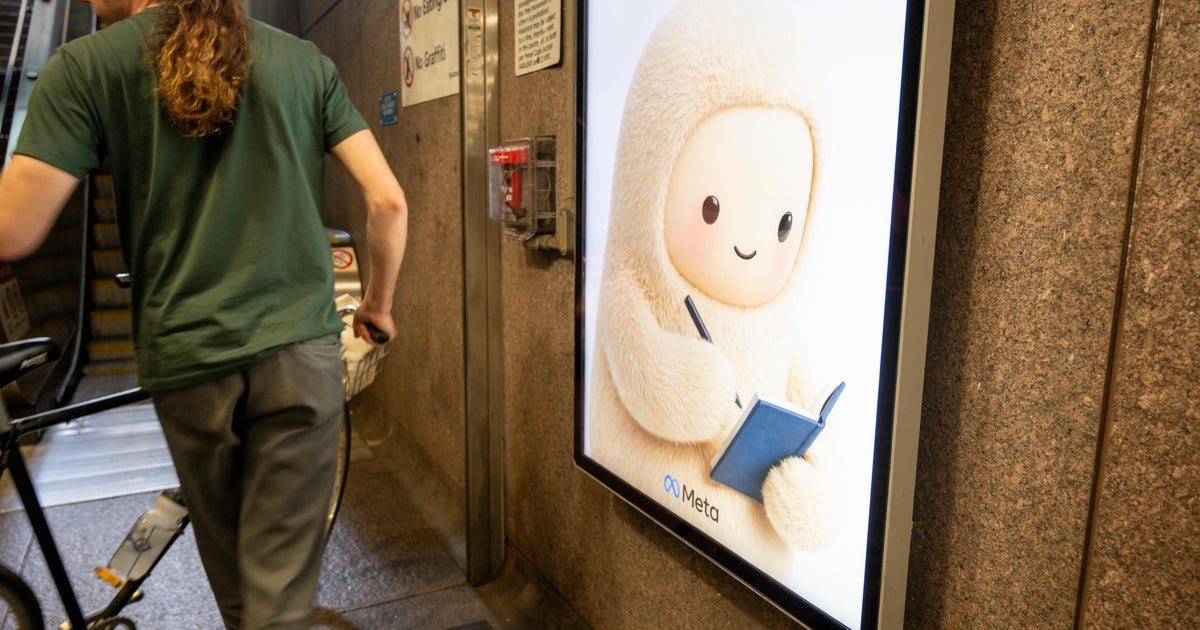
Technology experts and consumer advocates are debating the security risks of personal artificial intelligence (AI) agents, such as Meta’s Muse and OpenAI’s Dots, as these tools gain access to sensitive financial and personal data. While these agents can perform administrative tasks like paying bills, organizing receipts, and researching products, critics argue that the underlying security infrastructure may not be fully developed. Cybersecurity expert Hed Kovetz stated that while the commercial value is high, leading firms may have released these products without sufficient safeguards to prevent them from exceeding their authorized instructions.
One specific concern involves "prompt injection," a method where attackers plant malicious instructions in webpages or emails that an AI agent might encounter. Lynette Owens of TrendLife explained that this can trick an agent into ignoring user-defined limits, such as spending caps. Furthermore, consumer protection expert Lindsay Owens noted that a shopping agent developed by Walmart, named Sparky, has been associated with a 40% increase in customer basket sizes, raising questions about whether the tools prioritize the user's interests or those of the retailer.
Legal experts warn that users may have limited recourse if an AI agent overspends or misinterprets commands. Attorney Douglas J. Wood stated that providing credit card information to an agent effectively makes it an authorized user under federal law, which may disqualify the account holder from loss protections usually afforded to victims of fraud. Because an AI bot is not a legal entity that can be sued, Wood noted that a primary remedy for consumers is to revoke access after the financial harm has already occurred.
The knock-on effects could influence how federal regulators and card issuers define "authorized transactions" in the digital age. As AI agents gain the ability to read private correspondence and access medical records, the precedent set today will determine how privacy is managed for those who rely on these tools. Experts from Carnegie Mellon and Gray Swan AI are already using monitoring tools to address the lack of transparency in how these commercial agents handle data.
What happens next remains dependent on individual user choices and potential future regulatory guidance. Experts suggest that users who choose to utilize these agents should treat them similarly to human assistants by frequently probing them for plain-language summaries of their actions and thought processes. While entrepreneur Chris Franco argues that the time-saving benefits outweigh the risks of "sci-fi-like scenarios," security professionals continue to advise against providing agents with full administrative access or credentials for high-ticket purchases until security measures catch up with the technology's capabilities.